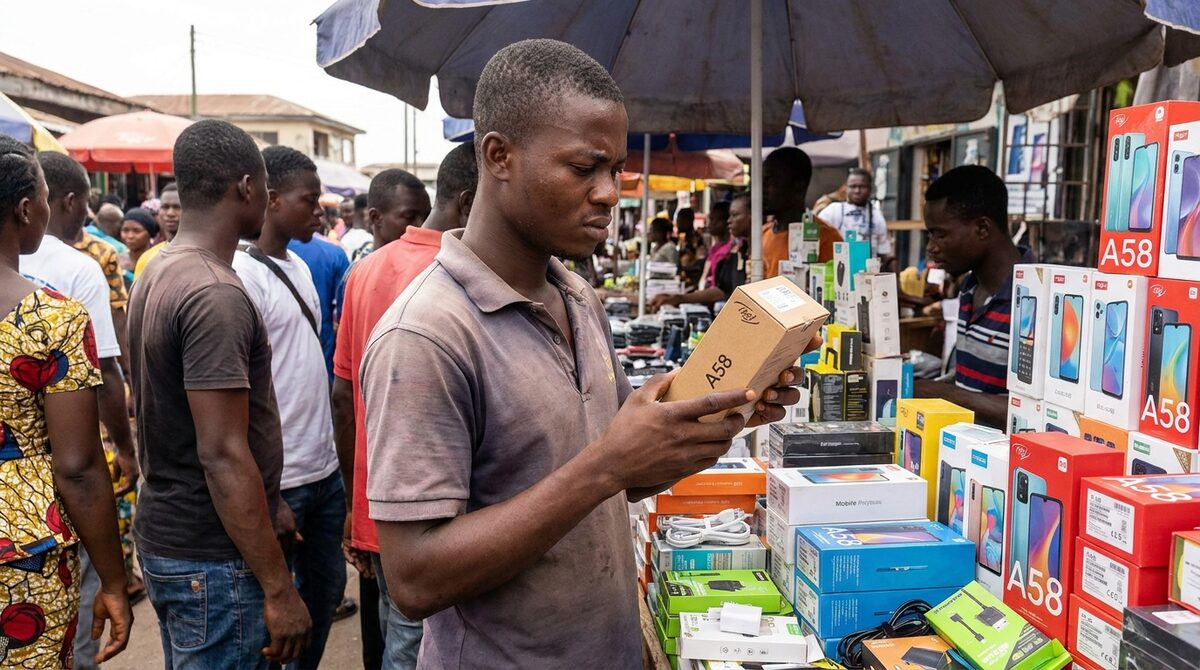
Millions of budget Android smartphones sold across Ghana and West Africa arrive with malicious software already embedded in the firmware — before the buyer ever turns the device on. This is not a software glitch or user error. It is a deliberate, profitable supply chain operation that security researchers have been documenting for years.
The problem is not limited to obscure brands. Devices bearing names that superficially resemble established manufacturers, as well as entirely unbranded handsets, flood markets in Accra, Kumasi, Tamale, and beyond — often priced between 150 and 400 Ghana Cedis. That affordability is the point. And it is also the vulnerability.
The Supply Chain Nobody Talks About
To understand how malware ends up on a phone before it is purchased, it is necessary to understand how budget Android phones are manufactured and distributed. Most low-cost Android devices sold in Ghana are not produced locally. They originate from factories in Shenzhen, China, where manufacturers produce handsets under white-label agreements.
White-labeling means a factory produces a generic device, and a brand — sometimes a regional distributor, sometimes a fictitious company — applies its own name and packaging. The Android operating system installed on these devices is often a heavily modified version of Android Open Source Project (AOSP), not the certified version that Google audits.
At one or more points along this chain — at the factory, during firmware customization, at a regional distribution warehouse, or even at a local wholesaler — malicious code is inserted into the system partition of the operating system.
Who Profits From Pre-Installed Malware
The Ad Fraud Economy
One of the most common forms of pre-installed malware found on budget African handsets is ad fraud software. These applications run invisibly in the background, simulating clicks on advertisements and generating fraudulent revenue for operators who have purchased ad impressions.
The device owner sees only the consequences: a phone that drains its battery faster than expected, consumes mobile data at an alarming rate, and runs slowly. In a country where mobile data is a significant household expense, the financial damage to consumers is real and measurable.
Research firm Upstream estimated in a published investigation that a single infected device can consume gigabytes of mobile data per month conducting invisible ad fraud — data costs that fall entirely on the consumer.
Subscription Fraud
A second category of malware found on these devices is designed to subscribe users to premium SMS or mobile billing services without their knowledge. Mobile carriers in Ghana and across West Africa offer services billed directly to a user's airtime balance — a convenient payment system that malware operators have learned to exploit.
The malware silently requests subscriptions, intercepts the confirmation messages sent by the carrier to authorize the charge, and suppresses those messages so the user never sees them. The airtime balance decreases. The user assumes their credits were consumed by calls or data. The fraud goes undetected.
"The target is not someone with a high-end device and a bank account. The target is someone spending their last few cedis on airtime to stay connected. The economics of this fraud depend on volume and invisibility." — Paraphrased from Upstream Security's published threat analysis on sub-Saharan Android fraud operations.
Data Harvesting for Resale
Some pre-installed applications on these devices function as spyware, collecting contact lists, SMS messages, location data, browsing history, and installed application lists. This data is transmitted to remote servers and sold to data brokers or used to build profiles for targeted fraud campaigns.
In 2026, as Ghana's digital financial ecosystem has grown substantially — with mobile money platforms like MTN MoMo and Vodafone Cash deeply embedded in daily commerce — this type of data harvesting carries increasingly serious consequences. A contact list combined with transaction behavior data is valuable to both advertising networks and criminal operations.
Common Myths About Pre-Installed Malware — Corrected
Myth: Installing an Antivirus App Will Fix It
This is one of the most widely held misconceptions about device security in consumer markets. Antivirus applications operate within the user-accessible portion of Android. Malware embedded in the system partition operates at a level that standard security applications cannot reach, modify, or remove.
Installing an antivirus app on a device with firmware-level malware is comparable to installing a lock on the front door of a house where the intruder is already living in the walls. The antivirus may detect the malware, report it, and warn the user — but it cannot eliminate it without system-level access.
Myth: Only Unbranded Phones Are Affected
Security research has consistently shown that the firmware tampering problem extends to devices carrying recognizable regional brand names. In some documented cases, phones bearing names nearly identical to major manufacturers — with one letter changed or a logo subtly altered — have been found to carry pre-installed malicious system applications.
The determining factor is not the brand name on the box. It is whether the device received a clean, certified firmware build and whether the supply chain between manufacturer and consumer was secure. For most budget handsets entering Ghana through informal import channels, neither condition is reliably met.
Myth: A Factory Reset Removes the Problem
As noted earlier, factory resets restore a device to the state defined by its firmware. If the malware is written into the firmware — specifically into the system partition, which the reset process does not touch — the device returns to an infected state after every reset.
This misunderstanding leads many Ghanaian consumers to cycle through repeated factory resets, each time believing the problem has been resolved, and each time watching the same issues return within days or weeks.
How to Identify a Compromised Device
While complete certainty requires technical analysis, several warning signs indicate a device may be carrying pre-installed malicious software. Consumers and small business owners in Ghana should examine their devices for the following indicators.
- Unexplained data consumption: If mobile data depletes faster than usage patterns justify — particularly overnight when the device is idle — background processes are likely transmitting data without authorization.
- Airtime balance decreasing without calls or data usage: Unauthorized premium subscription charges are a documented behavior of malware targeting African mobile users.
- Unfamiliar applications that cannot be uninstalled: System-level applications installed as part of infected firmware often appear in the app list without a functioning uninstall option — only a grayed-out "Disable" button.
- Device overheating during idle periods: Sustained background processing for ad fraud or data transmission generates heat even when the user is not actively using the device.
- Pop-up advertisements appearing outside of any browser or app: Adware embedded at the system level can serve advertisements across the entire operating system interface.
- Slower performance over time on a relatively new device: Background malware consumes processing resources, causing noticeable degradation within weeks of purchase.
Practical Steps Consumers Can Take Right Now
Verify Google Play Protect Certification
Google maintains a public list of Android devices that have passed its certification process. Certified devices receive a legitimate, audited version of Android with verified pre-installed applications. A device that fails this certification is operating outside Google's oversight — and is significantly more likely to carry unauthorized system software.
Consumers can check whether a device is certified by opening the Google Play Store, navigating to the settings menu, and looking for the "Play Protect certification" entry. A status reading "Device is certified" provides a meaningful — though not absolute — indication that the firmware has not been tampered with downstream of the factory.
Purchase From Authorized Retailers
The informal market for electronics in Ghana — roadside stalls, open-air markets, and unregistered mobile phone shops — represents the highest-risk purchasing environment. Authorized distributors and registered electronics retailers are more likely to source devices through traceable supply chains.
Brands that maintain official distributor networks in Ghana — including Samsung, Tecno, Itel, and Infinix — provide a more reliable chain of custody. This does not guarantee a clean device, but it substantially reduces exposure to supply chain tampering.
Monitor Mobile Data and Airtime With Carrier Tools
MTN Ghana, Telecel (formerly Vodafone Ghana), and AirtelTigo all provide USSD codes and mobile applications that allow subscribers to review active premium subscriptions and recent data usage. Regularly checking these records — weekly rather than monthly — allows users to detect unauthorized charges before significant losses accumulate.
Unrecognized subscriptions can be canceled directly through the carrier. MTN Ghana, for instance, provides a dedicated short code for reviewing and canceling all active premium service subscriptions.
Use Android's Built-In Application Audit
Navigating to Settings → Apps → See All Apps and sorting by storage or permissions reveals applications with unusual access to SMS, contacts, location, and internet connectivity. Any application the user does not recognize that holds permissions to read SMS messages or make calls warrants immediate investigation.
The Regulatory and Industry Response
Ghana's National Communications Authority (NCA) has the authority to regulate device type approval — the process by which mobile devices are certified for use on Ghanaian networks. Tightening type approval requirements to include firmware integrity verification would create a meaningful barrier against compromised devices entering the market legally.
Several African nations are moving in this direction. Nigeria's National Information Technology Development Agency (NITDA) has published guidelines on minimum device security standards. South Africa's ICASA has taken enforcement action against importers of uncertified devices. Ghana's regulatory apparatus has the tools — the question is whether enforcement keeps pace with the scale of the problem.
On the industry side, Google's Android certification program remains the most accessible protection mechanism for consumers. Expanding awareness of Play Protect certification among Ghanaian buyers — through carrier messaging, point-of-sale education, and media coverage — represents a cost-effective intervention that does not require legislative action.
The digital economy in Ghana depends on mobile connectivity. When the devices enabling that connectivity arrive pre-compromised, the foundational trust required for mobile commerce, digital banking, and e-government services is undermined at the hardware level — before the user has made a single transaction.
What the Market Needs to Change
The pre-installed malware problem in Ghana's budget smartphone market will not resolve itself through consumer awareness alone. It requires coordinated action across three levels: regulatory enforcement at the point of import, industry accountability from distributors and retailers, and informed demand from consumers who understand what certified devices look like.
The assumption that a phone is safe simply because it was purchased in a shop is one that the evidence — gathered by security researchers, mobile carriers, and cybersecurity firms across multiple years — firmly contradicts. In 2026, with mobile money, digital identity, and financial services increasingly dependent on smartphone access, the stakes of that assumption are higher than ever.
Ghanaian consumers deserve devices that work for them from the moment they are powered on. Holding importers, distributors, and regulators accountable for the security of devices entering the market is not a niche technical concern — it is a consumer rights issue with direct economic consequences for millions of people. The conversation needs to move from technical circles into mainstream public discourse, and it needs to happen now.